Self-hosted SSL monitoring with Docker
Same checker. You run the box, or we do.
Self-hosted (AGPL, SQLite)
The open-source app lives at github.com/einperegrin/sslert. Data is local SQLite. Auth is a bearer token you create in the container. No Stripe, no hosted Postgres.
One-liner from a clone of the repo:
cp .env.example .env
docker compose up --build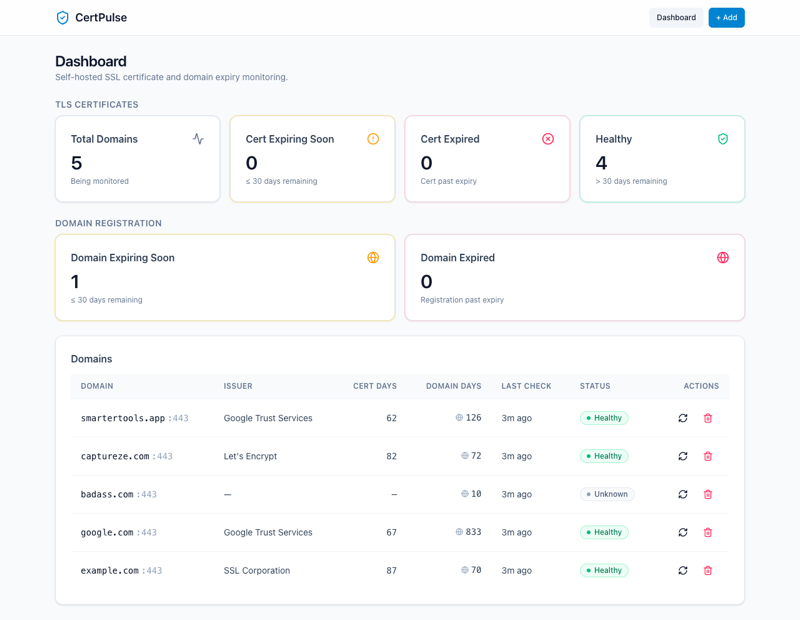
Dashboard: http://localhost:5173. Create a token:
docker compose exec api npm run token:create -- --label "admin"Optional: set RESEND_API_KEY and ALERT_EMAIL_TO for email. Leave them blank and alerts go to stdout. Telegram, Slack, ntfy, and HTTPS webhooks work without us in the path.
You are responsible for upgrades, disk, and not exposing the API. The licence is AGPL v3 — if you modify and offer it as a network service, you owe source.
Managed (sslert.com)
If you do not want to run Compose, the hosted product is sslert.com. Free: 10 domains, email, daily checks. Pro: $15/month or $150/year, 50 domains, all channels, 15-minute checks. No Team plan is sold. Sign in is a normal account, not a local token.
The public checker at sslert.com/check is the same live handshake, without an account. Use it to see a host before you decide whether to self-host or watch it on the managed side.
Self-hosted and managed share the TLS check. They do not share a database. Pick one place to be the source of truth for a hostname.